Livestream Internet Failover Setup That Holds
A corporate livestream can have excellent cameras, clean audio, polished graphics, and an experienced crew, then lose its remote audience because one internet connection becomes unstable.
A reliable livestream internet failover setup is designed and tested before an executive walks onstage. The production team needs to know what happens when upload bandwidth drops, packet loss increases, a venue circuit disappears, or the primary network can no longer maintain the stream.
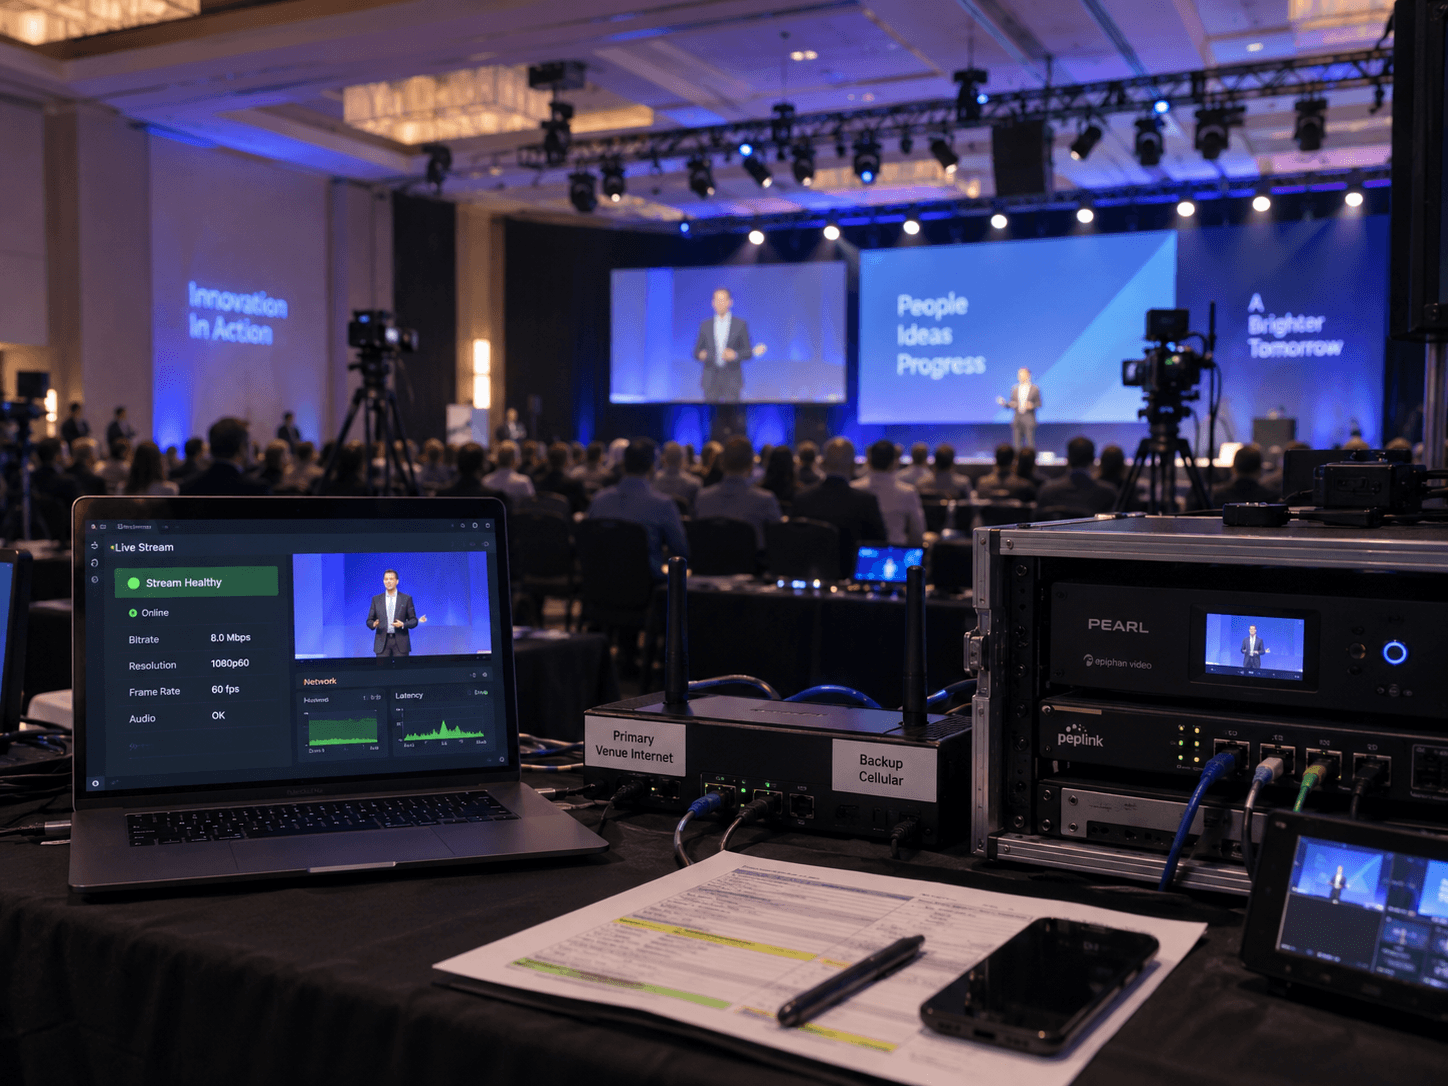
For corporate conferences, product launches, executive webcasts, and hybrid events, internet redundancy should be treated as part of the production system rather than an emergency hotspot sitting next to the encoder.
To plan a livestream internet failover setup that actually protects the show, start with independent connectivity, understand how the stream reacts when paths change, and test the failure deliberately before doors open.
Livestream Internet Failover Setup: What Actually Needs Protection?
The goal is not simply to keep an encoder connected to the internet.
The complete delivery chain may include:
- Production switcher output
- Streaming encoder
- Local production network
- Router or bonding device
- Primary internet circuit
- Backup internet path
- Transport protocol
- Cloud or receiving endpoint
- Streaming platform
- Embedded player
- Viewer connection
A failure at any point in that chain can affect the audience.
This is why a good internet redundancy plan looks beyond the WAN connection itself.
Internet Failure Does Not Always Mean Internet Disconnection
One of the most important things to understand is that an internet circuit can technically remain online while becoming unusable for live video.
Conditions may deteriorate through:
- Reduced upload throughput
- Packet loss
- Increasing latency
- Jitter
- Congestion
- Routing problems
The encoder may still report that it is connected while viewers experience reduced quality, audio interruptions, buffering, or complete playback failure.
This matters because a failover system that reacts only after the primary connection disappears completely may respond too late.
At the same time, switching paths every time the network has a brief fluctuation can create additional instability.
Failover behavior should therefore match the encoder, protocol, network architecture, and consequence of interruption.
Start With the Actual Streaming Bitrate
Internet planning should begin with the stream being transmitted rather than a single speed-test number.
If the encoder is transmitting a 10 Mbps stream, a connection that happens to test at 12 Mbps upload does not provide meaningful operating margin.
The available connection may also need to support:
- Encoder overhead
- Bitrate variation
- Remote presenters
- Confidence monitoring
- Captioning services
- Platform monitoring
- Control traffic
The primary connection should have enough sustained capacity to operate comfortably instead of constantly approaching its limit.
A Speed Test Is Only One Part of Testing
Tools such as Ookla Speedtest are useful for quickly checking connectivity, but a short speed test does not recreate a multi-hour livestream.
Production testing should also evaluate:
- Sustained upload performance
- Packet loss
- Latency
- Jitter
- Actual encoder behavior
- Actual destination-platform ingest
Whenever practical, test the actual encoder from the actual production location using the actual streaming destination.
Use a Dedicated Wired Connection as the Primary Path When Possible
For a high-visibility corporate webcast, a managed wired internet connection is generally preferable as the primary path when the venue can provide one.
Before show day, confirm:
- Physical handoff location
- Connector type
- Expected upload capacity
- Static or DHCP addressing
- Firewall restrictions
- Device registration
- Support contact
- Service escalation procedure
Also ask what the venue means by “dedicated.”
A production VLAN can isolate your devices from guest traffic while still sharing upstream infrastructure with other venue services.
Do Not Treat Venue Wi-Fi as Equivalent to a Dedicated Circuit
Venue Wi-Fi can be useful for secondary tasks and occasionally as an emergency connectivity option.
But its RF environment can change dramatically once attendees enter the room.
Hundreds or thousands of phones, laptops, and other devices may begin competing for airtime.
That does not mean Wi-Fi can never carry a stream.
It means that a high-stakes production should understand and test the risks rather than assuming that strong Wi-Fi signal bars equal reliable contribution bandwidth.
Build Independent Internet Paths
Two connections are not necessarily redundant simply because they use different cables.
Two Ethernet ports from the same venue network may still share:
- The same router
- The same switch infrastructure
- The same fiber entrance
- The same upstream internet provider
- The same building power
A single failure can therefore remove both paths.
Better redundancy comes from reducing shared dependencies.
A production may use:
- Dedicated venue hardline
- Independent cellular connectivity
- A second wired provider where available
- LEO satellite connectivity where appropriate
- Bonded combinations of multiple WAN technologies
The correct design depends on the visibility of the event and the consequences of losing the stream.
Understand Failover, Load Balancing, and Bonding
These terms are often used interchangeably, but they describe different behaviors.
WAN Failover
With conventional WAN failover, the primary connection handles traffic until the router determines that it has failed or become unusable.
The router then moves traffic to another WAN.
This provides redundancy, but an existing stream session may need to reconnect after the route or public IP address changes.
Load Balancing
Load balancing distributes different network sessions across multiple internet connections.
It can help prevent one circuit from carrying every device and application, but it does not automatically mean that a single livestream is using all available connections simultaneously.
Hot Failover
Some managed networking systems maintain tunnels that allow active sessions to survive the loss of one underlying WAN path.
For example, Peplink SpeedFusion supports functions including Hot Failover, WAN Smoothing, and packet-level bandwidth bonding.
True Connection Bonding
Bonding combines multiple internet connections through compatible hardware, software, or a managed transport service.
Rather than waiting for one circuit to fail and then starting another, the system can distribute traffic across multiple active connections.
This can provide greater resilience because the stream is not completely dependent on one underlying path.
LiveU Reliable Transport (LRT), for example, is designed to bond multiple IP connections including cellular and traditional wired or wireless networks for resilient live-video transmission.
Bonding is not simply plugging Ethernet and Wi-Fi into the same encoder.
The system needs compatible transport technology that can combine and reconstruct the traffic appropriately.
Failover and Bonding Solve Different Problems
A lower-risk internal meeting may be adequately protected by a reliable wired connection plus router-level failover.
A flagship product launch, investor webcast, or executive broadcast may justify a bonded transmission workflow designed to maintain session continuity when an underlying network changes.
Neither approach eliminates the need for testing.
The production still depends on:
- Encoder configuration
- Power
- Network hardware
- Transport endpoint
- Streaming platform
- Correct credentials
- Viewer playback
The Streaming Protocol Matters Too
The transport protocol can influence how the contribution feed behaves over an imperfect network.
Traditional RTMP remains common for delivering streams into many web platforms.
Other contribution workflows may use technologies such as SRT.
Secure Reliable Transport (SRT) was designed for secure, reliable video transport across unpredictable public networks and includes mechanisms intended to recover from network impairments such as packet loss and jitter.
Using a resilient protocol does not create redundant internet by itself.
It can improve transport behavior, but losing the only internet path still removes connectivity.
Plan Cellular Backup as Seriously as the Primary Connection
Cellular is valuable because it can provide infrastructure diversity from a venue hardline.
But cellular performance can change as the environment changes.
Test from the exact production location whenever possible.
Consider:
- Carrier diversity
- Indoor signal penetration
- Antenna placement
- Modem placement
- Available 4G/5G service
- Network congestion
- Expected attendee count
A cellular path that performs perfectly in an empty ballroom at 7:00 AM may behave differently when thousands of attendees are using nearby cellular networks during the keynote.
Control the Local Production Network
The streaming encoder should preferably operate on a controlled production network rather than sitting directly on a general venue or guest network.
A production router provides a defined gateway and allows the technical team to control which devices have internet access.
Avoid unnecessary traffic from:
- Cloud synchronization
- Automatic software updates
- Personal devices
- Unmanaged laptops
- Large background file transfers
If remote guests, cloud graphics, teleprompter systems, or confidence-return systems also require internet, document those dependencies so they do not unexpectedly compete with the primary stream.
Power Redundancy Is Part of Internet Redundancy
A redundant WAN design can still have one very simple point of failure: power.
If the encoder, router, modem, and network switch all connect to the same unprotected power strip, losing that circuit removes every internet path at once.
Depending on the production risk, consider appropriate UPS protection for:
- Streaming encoder
- Router
- Network switch
- Cellular modem
- Bonding appliance
Verify expected battery runtime rather than simply confirming that a UPS is installed.
Test the Failover by Actually Breaking the Primary Connection
This is one of the most important steps.
A diagram showing redundant connections does not prove that the redundancy works.
During technical rehearsal, intentionally disconnect the primary connection.
Then watch:
- Encoder status
- Outgoing bitrate
- Router or bonding status
- Transport receiver
- Streaming-platform ingest
- Public viewer player
- Program audio
Measure what the audience actually experiences.
Then Test Recovery Back to the Primary Path
Restoring the main circuit deserves testing too.
Automatic failback is not always desirable.
If a primary circuit returns for ten seconds but remains unstable, immediately moving the stream back can cause another interruption.
For some productions, it is safer to remain on the stable backup path until an operator verifies that the primary connection has recovered.
The procedure should be decided before the live show.
Monitor the Stream From Outside the Production Network
Looking at the encoder preview is not the same thing as verifying the audience experience.
A strong workflow includes confidence monitoring of the actual destination.
Whenever practical, view the public or authenticated player through an internet connection independent from the production network.
This can reveal:
- Platform buffering
- Audio problems
- Incorrect ingest
- Playback failure
- Authentication issues
- Unexpected latency
The encoder may look completely healthy while the problem exists farther downstream.
Keep a Local Recording
A local recording does not prevent a livestream outage.
It protects the final content asset.
If the platform, internet path, or CDN experiences an interruption, a clean local program recording provides a version that can be uploaded, edited, redistributed, or archived afterward.
Recording and connectivity redundancy solve different problems, and both may be appropriate for a critical corporate broadcast.
Assign One Person to Own Connectivity
Internet failover can involve:
- Venue IT
- Streaming engineer
- Technical director
- Corporate IT
- Platform administrator
- Network provider
Before doors open, one technical person should clearly own the stream connectivity path.
That person should have:
- Circuit information
- Router access
- Platform credentials
- Venue IT contact
- Carrier information
- Backup procedure
- Escalation contacts
The show caller does not need every networking detail.
They need clear status language such as:
- Primary stable
- Backup armed
- Running on backup
- Primary restored
- Stream recovery in progress
Livestream Internet Failover Checklist
- Required streaming bitrate confirmed
- Primary upload capacity verified
- Sustained test completed
- Packet loss and latency checked
- Primary connection identified
- Backup connection identified
- Shared infrastructure investigated
- Cellular carrier diversity considered
- Router or bonding system configured
- Encoder tested on primary connection
- Encoder tested on backup connection
- Forced failover tested
- Failback procedure tested
- Destination platform verified
- Public player monitored
- Power protection verified
- Local recording tested
- Venue IT escalation contact confirmed
- Connectivity owner assigned
A Backup Connection Only Counts If It Has Been Tested
The goal of a livestream internet failover setup is not to build the most complicated network possible.
It is to identify the connectivity failures that could interrupt the event and build a practical recovery strategy around them.
Sometimes that means a dedicated hardline with a cellular backup.
Sometimes router-level WAN failover is enough.
For higher-risk productions, true bonded transport may provide the continuity the event requires.
What matters is that the paths are independent enough to be useful, the behavior is understood, and the production team has intentionally tested what happens when the primary connection disappears.
For additional planning, see our guide to building redundant AV systems for corporate keynotes.
Need Reliable Livestream Production for a Corporate Event?
AV Land provides corporate livestream production, video switching, encoding, camera production, network planning, recording, and technical direction for conferences, executive webcasts, product launches, and hybrid events throughout the San Francisco Bay Area and beyond.
Contact AV Land to discuss the requirements for your next livestream.
Livestream Internet Failover FAQ
What is a livestream internet failover setup?
It is a network design that provides another usable internet path when the primary connection fails or becomes unusable. Depending on the system, that may involve conventional WAN failover, hot failover, or bonded internet connectivity.
Is having two internet connections enough?
Not necessarily. If both connections depend on the same venue network, upstream provider, power source, or physical infrastructure, one failure may remove both. Useful redundancy should reduce important shared failure points.
What is the difference between failover and bonding?
Traditional failover moves traffic from one connection to another when the primary fails. Bonding uses compatible technology to combine multiple active connections into a coordinated transport path, potentially allowing traffic to continue when one individual link degrades or disappears.
Can I use a phone hotspot as my livestream backup?
A phone hotspot may provide emergency connectivity for some low-risk situations, but critical corporate broadcasts benefit from professionally managed cellular hardware, controlled networking, external antennas where needed, carrier diversity, and advance testing.
Is venue Wi-Fi suitable for livestreaming?
It depends on how the network is designed and managed. Shared attendee Wi-Fi is generally less predictable than a controlled wired connection because conditions can change significantly as the venue fills with devices.
Does SRT replace bonded internet?
No. SRT can improve video transport over imperfect networks, but it does not create a second internet connection. If the only available path disappears completely, the stream still loses connectivity.
Should failover be tested before every event?
For an important livestream, yes. The production team should verify both paths and deliberately test the actual failover process so they understand how the encoder, network, streaming destination, and viewer player react.